


As we speak, I’m thrilled to announce that Cisco Safe Entry – the inspiration to securing connectivity to all functions throughout your hyper-distributed surroundings – is mostly accessible. With Cisco Safe Entry, your end-users can do their greatest work, securely accessing any utility (net, SaaS, or personal) with one expertise, from anyplace.
Introduced in June at Cisco Reside – buyer response has been constant, sturdy, and optimistic. Their enthusiasm and intense curiosity sparked sturdy buyer engagement and fostered order momentum. With factors of presence (POPs) and buyer trials throughout all areas – Americas, EMEA and APJC – we’re selling the overall availability of the service.
Cisco Safe Entry is an evolution of Cisco Umbrella Safe Web Gateway (SIG), our premier cloud-delivered safety resolution for safe web entry. Cisco is growing a ‘step-up’ program to allow current SIG clients to reap the benefits of the expanded providers, together with the brand new ZTNA and VPNaaS capabilities.
What are we fixing for?
Let’s simply say it. Securing hyper-distributed environments is troublesome and complicated, with customers working just about anyplace and accessing a plethora of sources throughout the web, public SaaS apps, and personal apps, in information facilities and the cloud.
Forty-three % of surveyed IT/safety leaders report that distant/hybrid staff signify the best safety threat. And roughly fifty % of those self same leaders cite a wide range of the reason why staff are annoyed with utility entry.[i] These go hand in hand and contribute to unacceptable ranges of threat.
Clients want a wiser option to handle connectivity from something to anyplace, whereas concurrently defending in opposition to savvy, refined attackers. They need broad utility of zero belief ideas to extend granular management and safety. They usually need to decrease IT complexity and scale back safety software sprawl. Briefly, they need safety that’s higher for customers, simpler for IT, and safer for everybody.
Nevertheless, know-how alone can’t sufficiently reply these persistent challenges. Minimizing threat in trendy safety environments additionally depends upon empowering an distinctive consumer expertise and addressing IT complexity and inefficiency.
Cisco’s new-age strategy to SSE – Cisco Safe Entry
Whereas many distributors promote Safety Service Edge (SSE) options, most supply a group of disparate elements requiring a number of consoles and brokers. This merely shifts the complexity drawback to the cloud.
Cisco has been converging cloud-native safety performance for a few years and has taken a holistic strategy to SSE. Our single console is powered by a contemporary, zero belief centered structure to ship pin-point management and least privileged entry to the whole spectrum of functions. The absolutely unified set of core SSE capabilities embody zero belief entry (ZTA), safe net gateway (SWG), cloud entry safety dealer (CASB), firewall-as-a-service (FWaaS).
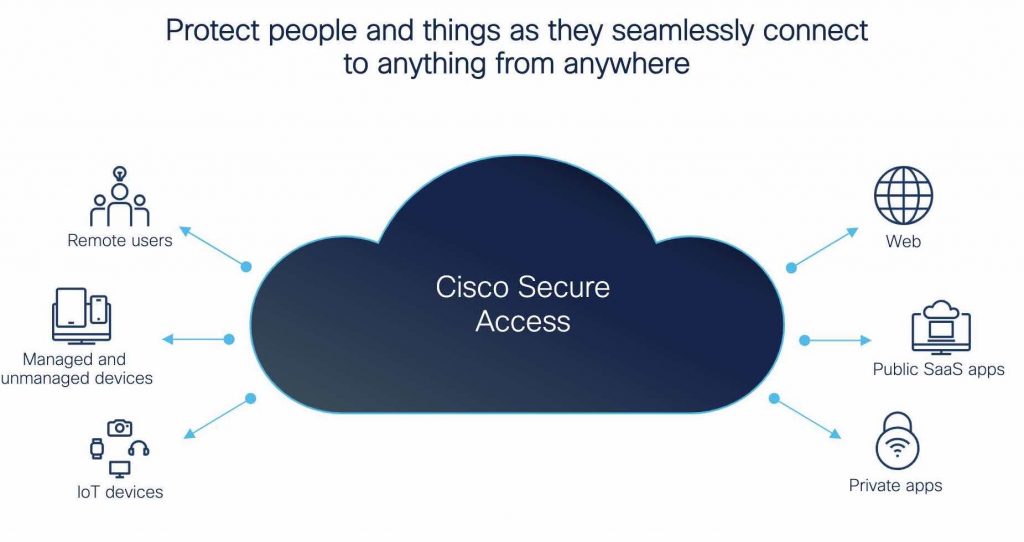
Cisco has prolonged properly previous the core to additionally embody DNS safety, Distant Browser Isolation (RBI), multi-mode Knowledge Loss Prevention (DLP), Digital Expertise Monitoring (DEM) insights, VPN as-a-Service (VPNaaS), in addition to a number of AI safety parts into a chic resolution with a single subscription. Our frictionless personal app entry delights finish customers. They only login and get to work. The advantages of least privilege and nil belief enforcement, single console, and a single agent empower the IT group to dam extra threats with much less effort. The result’s an answer that mitigates threat and drives larger productiveness for each customers and the IT group.
Why Cisco Safe Entry?
Zero Belief Entry (ZTA) Relay: Cisco’s complete ZTA personal entry know-how allows organizations to interrupt via the normal limitations of inflexible first era ZTNA options. Safe Entry makes use of new, excessive effectivity protocols (MASQUE and QUIC) and relay know-how. This allows hyper-granular zero belief management, bi-directional obfuscation, and improved efficiency whereas decreasing useful resource publicity and defending the total spectrum of personal functions.
Single agent: One simple to handle agent empowers a broad set of safety features to simplify the safety course of for managed units. Zero trust-powered clientless entry extends least privilege controls to BYOD and contractor units.
Single console: One unified console makes it simple to configure the broad set of Safe Entry features. One coverage engine reduces the hassle to safe web, SaaS, and personal app entry. Consolidated reporting improves detection and reduces investigation time. All these capabilities are supported by a contemporary, excessive pace, hybrid POP mannequin that gives world protection and speedy expandability.
Synthetic intelligence: Cisco has embraced AI and machine studying to show the huge Talos risk intelligence telemetry into quicker incident detection and stronger safety in opposition to each current and rising assault techniques. On the identical time, we offer management and safety to your customers and information once they entry AI functions. You possibly can detect and block the usage of particular AI apps. Moreover, you possibly can apply DLP insurance policies to guard delicate information equivalent to mental capital and supply code when customers are accessing public AI providers.
If you wish to scale back threat in your distributed surroundings, whereas growing consumer productiveness and empowering IT with a brand new stage of management and effectivity, go to Cisco Safe Entry. Begin your journey right this moment.
Sources
[i] “Keys to Profitable SSE: Supporting Consumer Expertise, IT Effectivity, and Safety Efficacy, Enterprise Technique Group (ESG), September 2023
We’d love to listen to what you suppose. Ask a Query, Remark Under, and Keep Related with Cisco Safe on social!
Cisco Safe Social Channels
Share:

