

Consultants from safety agency F5 have argued that cyber criminals are unlikely to ship new armies of generative AI-driven bots into battle with enterprise safety defences within the close to future as a result of confirmed social engineering assault strategies might be simpler to mount utilizing generative AI.
The discharge of generative AI instruments, akin to ChatGPT, have triggered widespread fears that democratization of highly effective giant language fashions might assist unhealthy actors all over the world supercharge their efforts to hack companies and steal or maintain delicate knowledge hostage.
F5, a multicloud safety and software supply supplier, tells TechRepublic that generative AI will lead to a development in social engineering assault volumes and capability in Australia, as menace actors ship the next quantity of higher high quality assaults to trick IT gatekeepers.
Soar to:
Social engineering assaults will develop and grow to be higher
Dan Woods, world head of intelligence at F5
International head of intelligence at F5, Dan Woods mentioned he’s much less fearful about AI leading to “killer robots” or a “nuclear holocaust” than some. However he’s “very involved about generative AI.” Woods says the most important menace dealing with each enterprises and folks is social engineering.
Australian IT leaders solely have to work together with a device akin to ChatGPT, Woods mentioned, to see the way it can mount a persuasive argument on a subject in addition to a persuasive counter argument — and do all of it with impeccable writing abilities. This was a boon for unhealthy actors all over the world.
“At the moment, one individual can socially engineer someplace between 40 and 50 folks at a time,” Woods mentioned. “With generative AI — and the power to synthesize the human voice — one legal might begin to social engineer nearly a vast variety of folks a day and do it extra successfully.”
SEE: DEF CON’s generative AI hacking problem explored the chopping fringe of safety vulnerabilities.
Issues Australian IT leaders have been instructing staff to think about crimson flags in phishing or smishing assaults, akin to issues with grammar, spelling and syntax, “will all go away.”
“We are going to see phishing and smishing assaults that won’t have errors any extra. Criminals will be capable of write in excellent English,” Woods mentioned. “These assaults might be properly structured in any language — it is vitally spectacular. So I fear about social engineering and phishing assaults.”
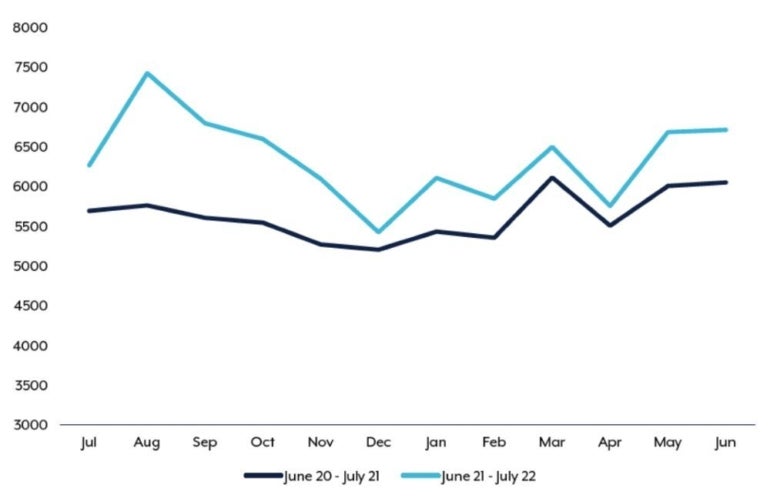
There have been already a complete of 76,000 cyber crime reviews in Australia within the 2021–22 monetary yr, based on Australian Cyber Safety Centre knowledge — up 13% on the earlier monetary yr (Determine A). Many of those assaults concerned social engineering strategies.
Determine A
Enterprises on the receiving finish of assault development
Australian IT groups can anticipate to be on the receiving finish of social engineering assault development. F5 mentioned the primary counter to altering unhealthy actor strategies and capabilities might be schooling to make sure staff are made conscious of accelerating assault sophistication resulting from AI.
“Scams that trick staff into doing one thing — like downloading a brand new model of a company VPN consumer or tricking accounts payable to pay some nonexistent service provider — will proceed to occur,” Woods mentioned. “They are going to be extra persuasive and enhance in quantity.”
Woods added that organizations might want to guarantee protocols are put in place, just like current monetary controls in an enterprise, to protect towards criminals’ rising persuasive energy. This might embrace measures akin to funds over a specific amount requiring a number of folks to approve.
Unhealthy actors will select social engineering over bot assaults
An AI-supported wave of bot assaults might not be as imminent because the social engineering menace.
There have been warnings that armies of bots, supercharged by new AI instruments, might be utilized by legal organizations to launch extra subtle automated assaults towards enterprise cybersecurity defences, increasing a brand new entrance in organisations’ warfare towards cyber criminals.
Risk actors solely rise to degree of safety defence sophistication
Nonetheless, Woods mentioned that, based mostly on his expertise, unhealthy actors have a tendency to make use of solely the extent of sophistication required to launch profitable assaults.
“Why throw extra assets at an assault if an unsophisticated assault technique is already being profitable?” he requested.
Woods, who has held safety roles with the CIA and FBI, likens this to the artwork of lock selecting.
“A lock selecting skilled may be outfitted with all the specialised superior instruments required to select locks, but when the door is unlocked they don’t want them — they are going to simply open the door,” Woods mentioned. “Attackers are very a lot the identical approach.
“We aren’t actually seeing AI launching bot assaults — it’s simpler to maneuver on to a softer goal than use AI towards, for instance, an F5-protected layer.”
Organizations can anticipate “a profound and alarming influence on legal exercise,” however not on all legal exercise concurrently.
“It isn’t till enterprises are protected by subtle countermeasures that we’ll see an increase in additional subtle AI assaults,” Woods mentioned.
Criminals will gravitate to much less cyber-aware Australian sectors
This lock selecting precept applies to the distribution of assaults throughout Australian enterprises. Jason Baden, F5’s regional vice chairman for Australia and New Zealand, mentioned Australia remained a profitable goal for unhealthy actors, and assaults have been shifting to much less protected sectors.
Jason Baden, regional vice chairman for Australia and New Zealand at F5
“F5’s buyer base in sectors like banking and finance, authorities and telecommunications, who’re the standard giant targets, have been spending some huge cash and loads of effort and time for a few years to safe networks,” Baden mentioned. “Their understanding could be very excessive.
“The place we’ve got seen the most important enhance over the past 12 months is in sectors that weren’t beforehand focused, together with schooling, well being and amenities administration. They’re actively being focused as a result of they haven’t spent as a lot cash on their safety networks.”
Enterprises will enhance cybersecurity defences with AI
IT groups might be simply as keen about utilizing the rising energy of synthetic intelligence to outwit unhealthy actors. For instance, there are AI and machine studying instruments that make human-like choices based mostly on fashions in areas akin to fraud detection.
To deploy AI to detect fraud, a buyer fraud file should be fed right into a machine studying mannequin. As a result of the fraud file comprises transactions tied to a confirmed fraud, it teaches the mannequin what fraud seems like, which it makes use of to establish future incidents of fraud in actual time.
SEE: Discover our complete synthetic intelligence cheat sheet.
“The fraud wouldn’t have to look precisely like earlier incidents, however simply have sufficient attributes in frequent that it will probably establish future fraud,” Woods mentioned. “We’ve been in a position to establish loads of future fraud and stop fraud, with some shoppers seeing return on funding in months.”
Nonetheless, Australian enterprises taking a look at utilizing AI to counter legal exercise should be conscious that the decision-making capabilities of AI fashions are solely pretty much as good as the information being fed into them: Woods mentioned organizations ought to actually be aiming to coach the fashions on “excellent knowledge.”
“To start with, many enterprises is not going to have a fraud file. Or in some circumstances they could have a number of hundred entries on it, 20% of that are false positives,” Woods mentioned. “However for those who go forward and deploy that mannequin, it would imply mitigating motion might be taken on extra of your good clients.”
Success might be as a lot about folks as instruments
IT leaders might want to guarantee they don’t overlook that individuals are one other key ingredient in success with AI fashions, along with having copious quantities of unpolluted knowledge for labelling.
“You want people. AI will not be able to be blindly trusted to make choices on safety,” Woods mentioned. “You want people who find themselves in a position to pour over the alerts, the selections, to make sure AI will not be making any false positives, which can have an effect on sure folks.”
Australia will proceed to draw consideration from menace actors
IT professionals might be in the course of a rising AI warfare between hackers and enterprises. F5’s Jason Baden mentioned that, resulting from Australia’s relative wealth, it would stay a closely focused jurisdiction.
“We are going to usually see threats come by first into Australia due to the financial advantages of that,” Baden mentioned. “This dialog will not be going away, it is going to be entrance of thoughts in Australia.”
Cybersecurity schooling might be required to fight threats
It will imply continued schooling on cybersecurity is required. Baden mentioned it is because “if it’s not generative AI right this moment, it might be one thing else tomorrow.” Enterprise stakeholders, together with boards, have to know that, regardless of cash invested, they may by no means be 100% safe.
“It needs to be schooling in any respect ranges of a company. We can not assume clients are conscious, however there are additionally skilled enterprise folks not uncovered to cybersecurity,” Baden mentioned. “They (boards) are investing the time to resolve it, and in some circumstances there’s a hope to repair it with cash or purchase a product and it’ll go away. However it’s a long-term play.”
F5 helps the actions of the Federal Authorities to additional construct Australian cybersecurity resilience, together with by six introduced Cyber Shields.
“Something that’s persevering with to extend consciousness of what the threats are is at all times going to be of profit,” Baden mentioned.
Much less complexity might assist win the warfare towards unhealthy actors
Whereas there is no such thing as a solution to be 100% safe, simplicity might assist organizations decrease dangers.
“Enterprises usually have contracts with dozens of various distributors,” Woods mentioned. “What enterprises needs to be doing is lowering that degree of complexity, as a result of it breeds vulnerability. That’s what unhealthy actors exploit on daily basis, is confusion resulting from complexity.”
By way of the cloud, for instance, Woods mentioned organizations didn’t got down to be multicloud, however the actuality of enterprise and life triggered them to be multicloud over time.
SEE: Australian and New Zealand enterprises are dealing with stress to optimize cloud methods.
“They want a layer of extraction over all these clouds, with one coverage that applies to all clouds, non-public and public,” Woods mentioned. “There’s now an enormous development in direction of consolidation and simplification to boost safety.”

