

Miragec/Getty Photos
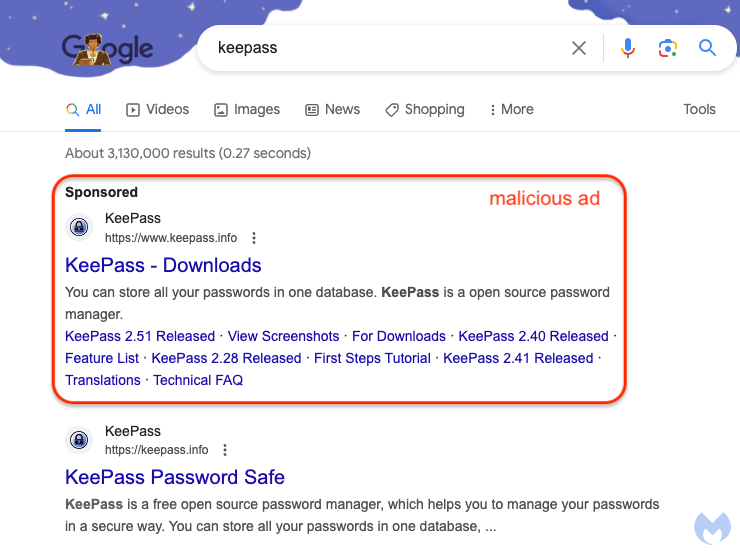
Google has been caught internet hosting a malicious advert so convincing that there’s a good probability it has managed to trick a few of the extra security-savvy customers who encountered it.
Malwarebytes
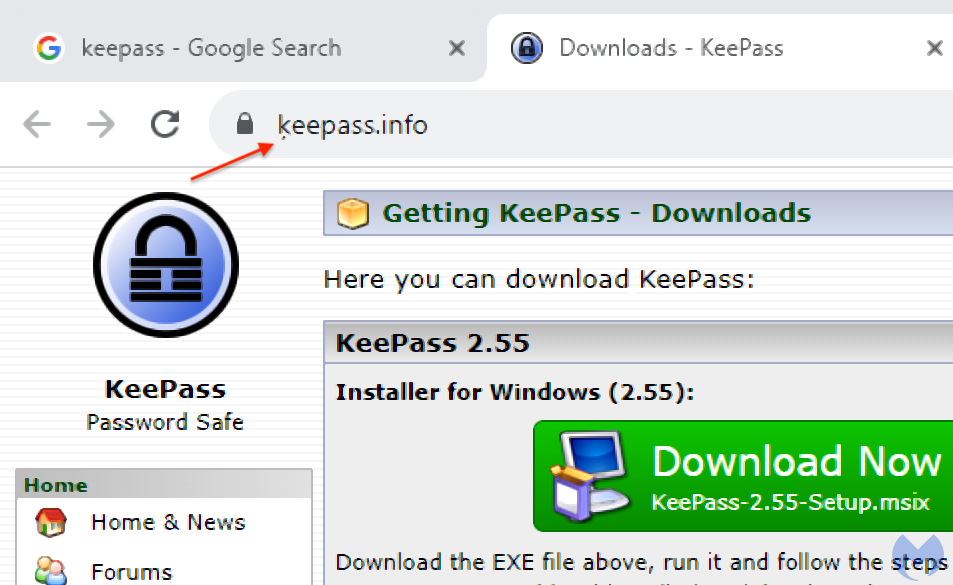
Trying on the advert, which masquerades as a pitch for the open-source password supervisor Keepass, there’s no solution to know that it’s faux. It’s on Google, in spite of everything, which claims to vet the adverts it carries. Making the ruse all of the extra convincing, clicking on it results in ķeepass[.]information, which when considered in an deal with bar seems to be the real Keepass web site.
Malwarebytes
A better hyperlink on the hyperlink, nonetheless, exhibits that the location is not the real one. In reality, ķeepass[.]information —at the very least when it seems within the deal with bar—is simply an encoded method of denoting xn--eepass-vbb[.]information, which it seems, is pushing a malware household tracked as FakeBat. Combining the advert on Google with a web site with an virtually equivalent URL creates a close to good storm of deception.
“Customers are first deceived by way of the Google advert that appears solely official after which once more by way of a lookalike area,” Jérôme Segura, head of menace intelligence at safety supplier Malwarebytes, wrote in a submit Wednesday that exposed the rip-off.
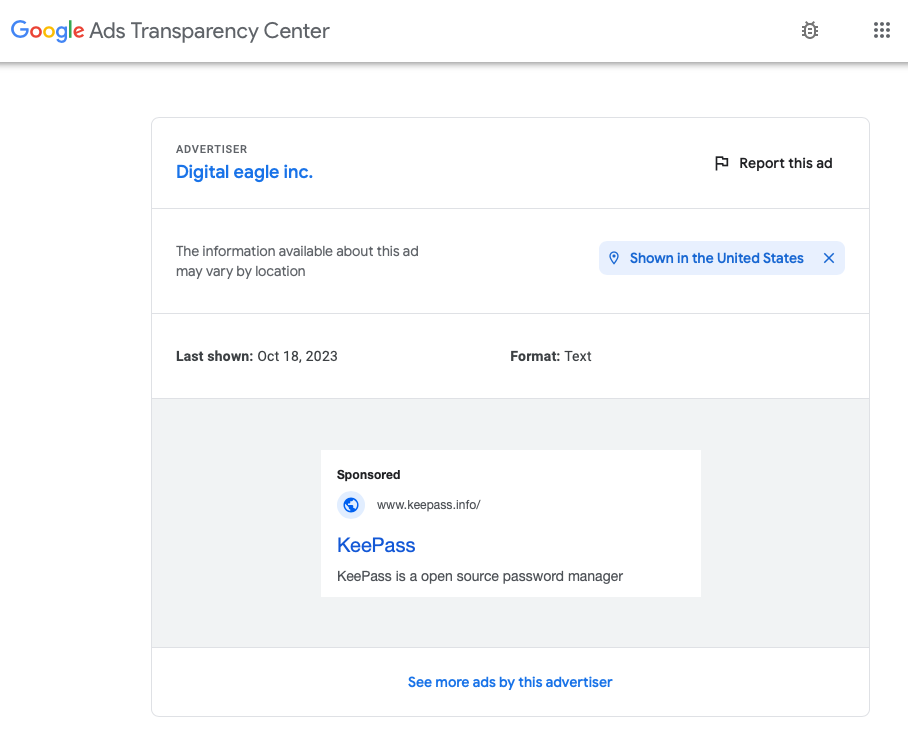
Info accessible via Google’s Advert Transparency Heart exhibits that the adverts have been operating since Saturday and final appeared on Wednesday. The adverts have been paid for by an outfit known as Digital Eagle, which the transparency web page says is an advertiser whose id has been verified by Google.
Malwarebytes
Google representatives didn’t instantly reply to an e mail, which was despatched after hours. Previously, the corporate has stated it promptly removes fraudulent adverts as quickly as attainable after they’re reported.
The sleight of hand that allowed the imposter web site xn--eepass-vbb[.]information to seem as ķeepass[.]information is an encoding scheme often known as punycode. It permits unicode characters to be represented in customary ASCII textual content. Trying rigorously, it’s simple to identify the small comma-like determine instantly under the ok. When it seems in an deal with bar, the determine is equally simple to overlook, particularly when the URL is backed by a sound TLS certificates, as is the case right here.
Using punycode-enhanced malware scams has a protracted historical past. Two years in the past, scammers used Google adverts to drive folks to a web site that appeared virtually equivalent to courageous.com, however was, in actual fact, one other malicious web site pushing a faux, malicious model of the browser. The punycode method first got here to widespread consideration in 2017, when a Net software developer created a proof-of-concept web site that masqueraded as apple.com.
There’s no sure-fire solution to detect both malicious Google adverts or punycode encoded URLs. Posting ķeepass[.]information into all 5 main browsers results in the imposter web site. When unsure, folks can open a brand new browser tab and manually sort the URL, however that’s not all the time possible once they’re lengthy. Another choice is to examine the TLS certificates to verify it belongs to the location displayed within the deal with bar.

