

This assault despatched roughly 120,000 phishing emails to organizations worldwide with the objective to steal Microsoft 365 credentials.
We break down the specifics of EvilProxy, together with which accounts have been focused, and supply tips about defending what you are promoting from this risk.
Leap to:
What’s EvilProxy?
EvilProxy is a phishing-as-a-service equipment that was first uncovered by cybersecurity firm Resecurity in September 2022. This equipment has the flexibility to run phishing assaults with reverse proxy capabilities that allow it to steal credentials and bypass 2FA by deploying adversary-in-the-middle methods (Determine A).
Determine A
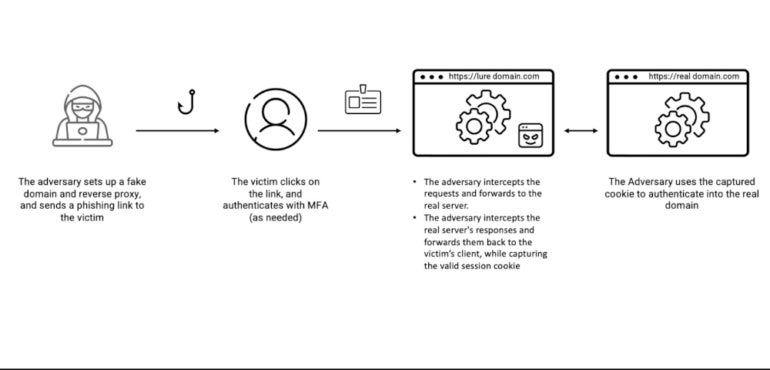
Any cybercriminal can purchase EvilProxy and begin utilizing it by way of a easy interface that enables the creation of phishing campaigns with customizable choices. The service units up a phishing web site in accordance with the chosen choices and is then able to go. When an unsuspecting consumer visits the phishing web page, they supply their credentials. The phishing web page then asks for the 2FA code for authentication to the service. As soon as offered, the code is instantly utilized by the equipment to get entry to the consumer’s account by opening a session.
Daniel Blackford, risk researcher at Proofpoint, informed TechRepublic that EvilProxy is bought in underground boards and Telegram channels, and added that “The fundamental model of EvilProxy prices a couple of hundred {dollars}, nevertheless it is determined by many parameters like: characteristic set, variety of focused customers, and so forth.”
EvilProxy assault chain
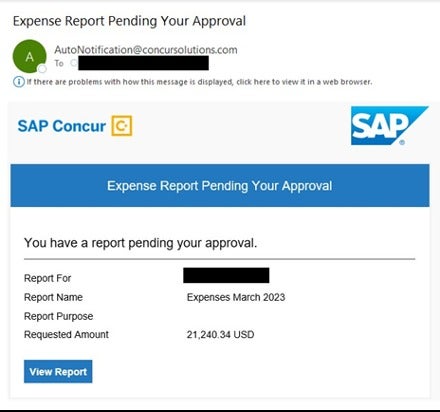
The assault marketing campaign begins with emails pretending to come back from recognized and trusted companies or manufacturers reminiscent of DocuSign, Adobe or Concur. The emails include a malicious hyperlink main the consumer to an open redirection at a reputable web site reminiscent of YouTube or Slickdeals (Determine B) in an try and keep away from detections on the e mail stage.
Determine B
A collection of redirecting web sites (Determine C) comply with in an unpredictable method, aiming to decrease the possibilities of discovery. The consumer lands on the EvilProxy phishing web site, which on this marketing campaign is a Microsoft login web page functioning as a reverse proxy.
Determine C
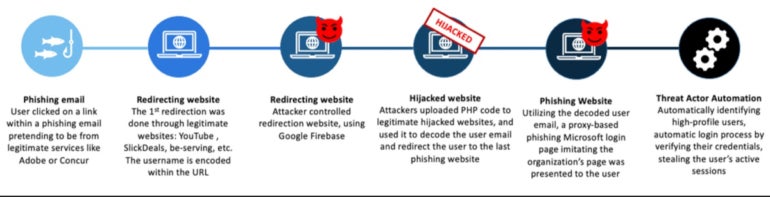
To cover the e-mail deal with of the sufferer whereas doing the redirections and keep away from automated scanning instruments detections, the attackers use a particular encoding and solely use compromised reputable web sites to add their PHP code to decode the e-mail deal with earlier than touchdown on the EvilProxy phishing web page.
Hundreds of high-value Microsoft cloud accounts focused
This assault marketing campaign despatched roughly 120,000 phishing emails to lots of of focused organizations worldwide between March and June 2023, with the objective to steal customers’ Microsoft 365 cloud credentials.
Based on Proofpoint, the record of focused customers consists of many high-value targets reminiscent of vice presidents and C-level executives from main corporations. The attackers ignored staff in decrease positions. As said by the researchers, it appears cheap to assume the risk actor used organizational data acquired from public sources to kind out who can be attention-grabbing.
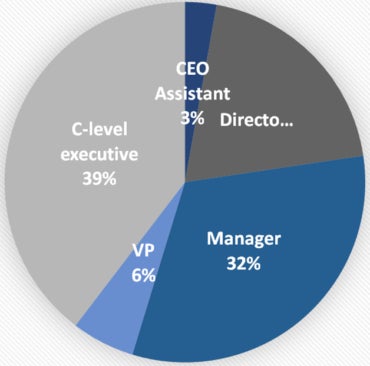
Statistics amongst lots of of compromised customers reveal that 39% have been C-level executives, of which 17% have been chief monetary officers and 9% have been presidents and chief govt officers. Managers have been 32% of the compromised customers (Determine D).
Determine D
Oddly, customers with a Turkish IP deal with have been redirected to the reputable internet web page, which suggests the risk actor may come from that nation or is actively ignoring any Turkish consumer account. Quite a few digital personal community IP addresses have been additionally redirected to the reputable web site as an alternative of the EvilProxy web page.
Whereas the objective of this assault marketing campaign stays unknown, this sort of assault usually results in monetary fraud or delicate information exfiltration. The risk actor may also promote entry to those high-value mailboxes to different cybercriminals.
Sustaining fraudulent entry to the mailboxes
As soon as an lively session is established on a compromised account, the risk actor provides its personal multifactor authentication technique within the Microsoft 365 parameters, including Authenticator App to it (Determine E).
Determine E
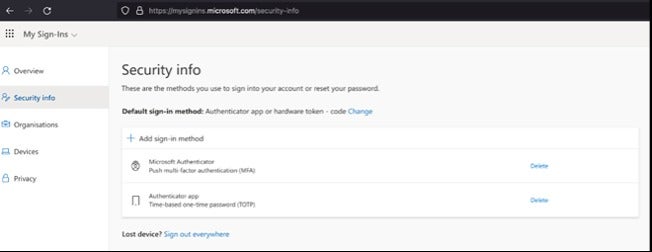
Afterward, the risk actor now not wants EvilProxy’s reverse proxy characteristic to log in to the compromised account and easily logs in with the credentials and a code offered on their very own Authenticator software.
How you can defend from this safety risk
Listed here are 4 suggestions for shielding towards the EvilProxy risk.
- Use e mail safety options to dam malicious emails despatched to staff.
- Practice staff to detect such phishing assaults.
- Deploy community safety options to attempt to detect phishing, malware or different threats.
- Run phishing assault simulations to assist IT elevate consciousness amongst staff.
It’s additionally suggested to make use of FIDO2-based bodily keys when doable as a result of that form of {hardware} securely shops a personal key that isn’t usually accessible to the attacker, even when the particular person is intercepting all communications between the consumer’s machine and the net service.
Disclosure: I work for Pattern Micro, however the views expressed on this article are mine.

